
Data residency
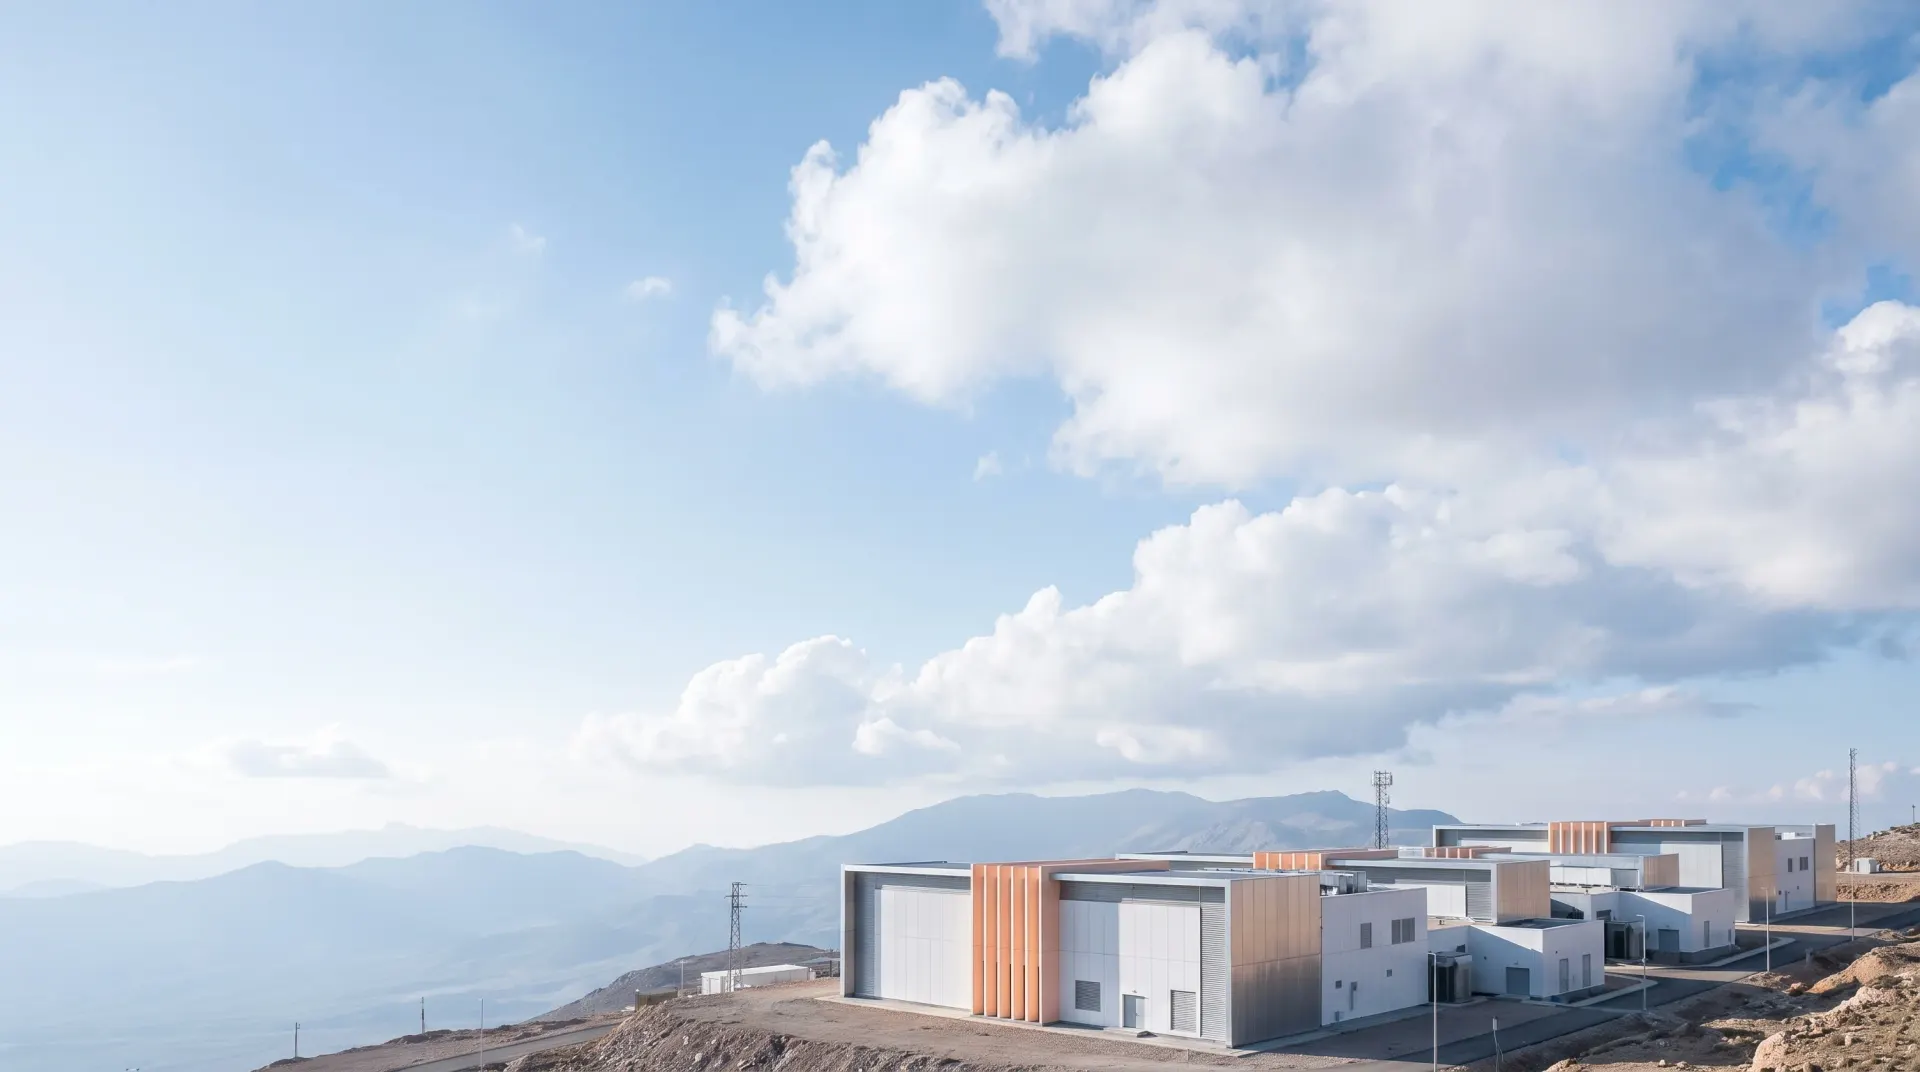
Place workloads on infrastructure in Türkiye, in the Istanbul (tr-ist-01) and Ankara (tr-ank-01) regions.
Infrastructure and security
Treat data residency, isolation, access and resilience as one responsibility model.
Overview
On PortvMind Cloud infrastructure, security is a set of decisions across layers. Region and physical infrastructure sit with PortvMind Cloud. Network and isolation are designed together in the target architecture. Identity, access and secret storage sit with the customer. Data protection is planned with Backup. Operations and incident response scope are defined in the contract.
Control areas cover data residency, isolation, identity and resilience.
Each control is applied together with the selected service and the target architecture.
Place workloads on infrastructure in Türkiye, in the Istanbul (tr-ist-01) and Ankara (tr-ank-01) regions.
Design project, virtual network, Router, Load Balancer and access boundaries together.
Define least privilege, separate credentials and a secret-storage approach.
Plan backup, retention and capacity together.
Responsibility splits into the PortvMind Cloud layer, the customer layer and controls planned together.
Infrastructure and control-plane responsibilities in the published service scope.
Account, access, operating system, application, data and configuration responsibilities.
Version, quota, network, backup, response and support scope are planned together.
Control plane
The diagram shows which layer a decision sits in and who owns it.
Infrastructure located in Türkiye · Istanbul tr-ist-01 · Ankara tr-ank-01
Project boundary · virtual network · Router · Load Balancer · external access rules
Least privilege · separate credentials · secret storage approach
Block · Object · snapshot · Backup
Monitoring · change · capacity · incident response · support scope
A service level commitment exists; its terms are defined in the contract.
The certificates are issued to vMind Bilgi Teknolojileri and are read together with the relevant service scope.
Information security management system
Information security controls for cloud services
Privacy information management system
Business continuity management system
IT service management system
Quality management system
Customer satisfaction and complaints handling
Occupational health and safety management system
Anti-bribery management system
Certificate holder: vMind Bilgi Teknolojileri
PortvMind Cloud is offered in two regions: Istanbul (tr-ist-01) and Ankara (tr-ank-01).
tr-ist-01Compute, storage and network resources are managed within the same project boundary.
tr-ank-01The second region; included in capacity planning for resilience and rollback objectives.
Related services
Virtual network, routing and access rules at the project boundary.
External access, health signals and traffic distribution.
Backup frequency and retention.
Data layer and long-term retention with full S3 API compatibility.
Related resources
We define isolation, access, data protection and response scope together with your target architecture.
Evaluate controls alongside the scope of each service.